
Industries · Regulated sectors
AI security for regulated industries: keep data in country
AI security for regulated industries means using AI while personal data stays in country and AI decisions can be shown to a regulator. DeepintShield can run entirely inside your environment, redacts personal data before it reaches a model and records decisions in a tamper-evident audit log, for banks, insurers, hospitals and public bodies.
- Self-hosted, with an air-gapped option
- Personal data redacted before the model
- Evidence you can verify and export
AI without governance, and AI with DeepintShield
Without governance
- No record of what the AI saw, said or did
- Customer and patient data sent to outside models
- Agents act with whatever access their keys allow
- No evidence ready when the regulator asks
With DeepintShield
- Requests, findings and agent decisions logged
- Personal data redacted before it leaves
- Each tool call allowed, denied or held for approval
- Evidence ready to export, inside your environment
AI security for regulated industries, sector by sector
Each sector has its own rules. Pick yours to see the controls that matter most.
Banking and financial services
For the RBI FREE-AI framework and India’s DPDP Act: customer data redacted before any model, with audit evidence.
AI security for banks
Government and public sector
Sovereign deployment: self-hosted or air-gapped, data kept in country and keys held by you.
Sovereign AI security
Healthcare
Medical record numbers and patient IDs redacted inline, access by role and an audit record of AI decisions.
AI security for healthcare
Global capability centres
One gateway for many teams, parent-company policies applied centrally and a budget for each team.
AI governance for GCCs
Sovereign deployment with no call-home
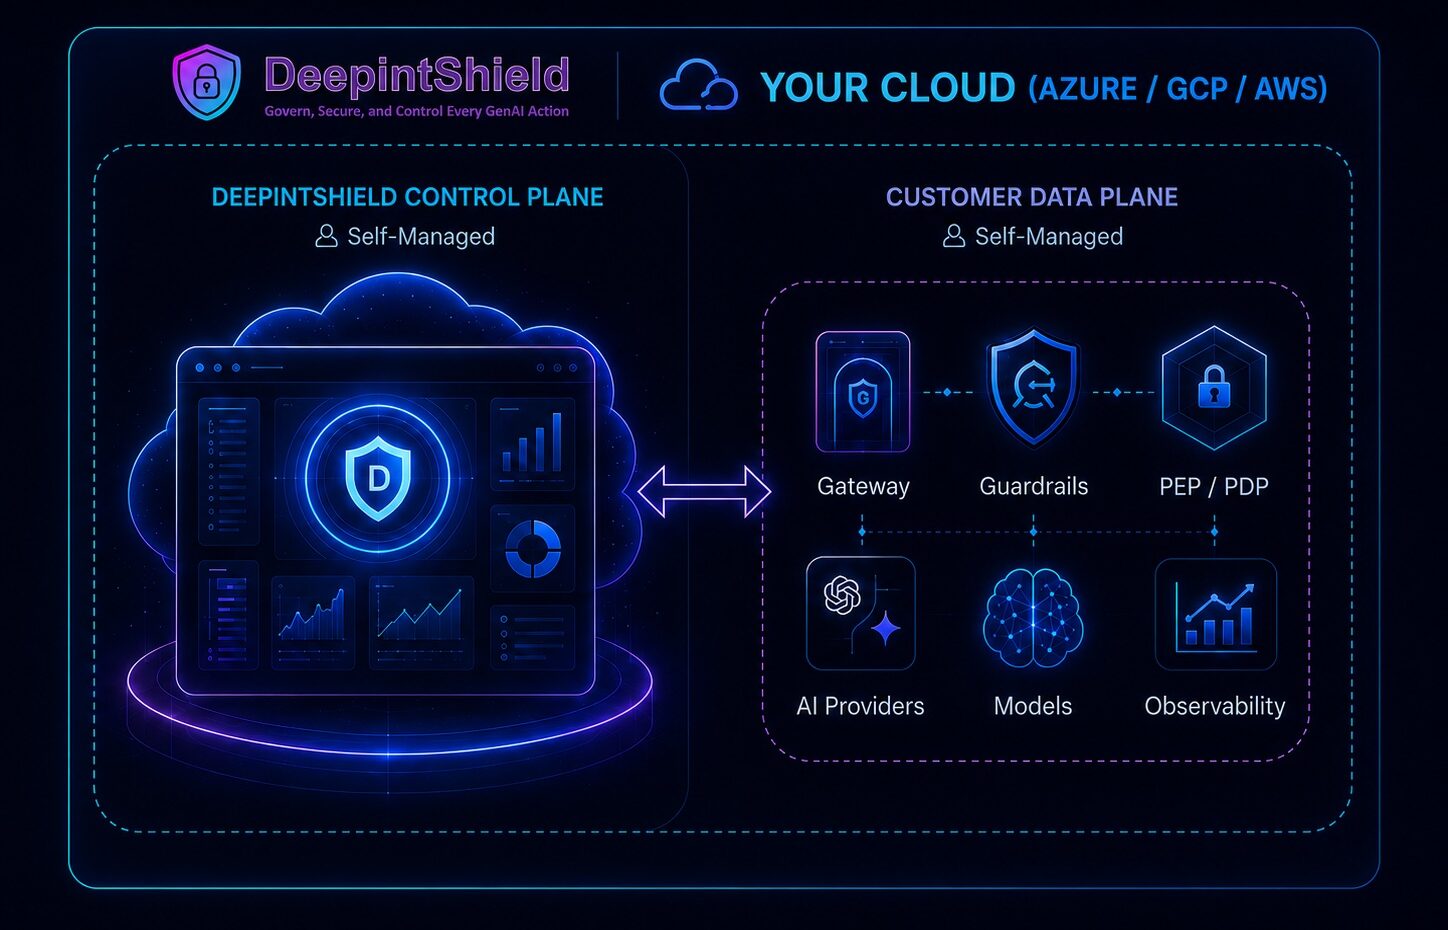
Run DeepintShield in your own cloud or data centre. Enterprise Self-Hosted keeps the control plane and the data plane in your environment, with an air-gapped delivery option. Enterprise VPC keeps prompts, responses, keys and audit data in your VPC; only signed configuration and aggregate counts cross one outbound-only link, and enforcement continues if that link drops. See self-hosted deployment for the details.
- Self-hosted in your cloud or data centre
- Air-gapped delivery on Enterprise Self-Hosted
- Bring your own keys from your KMS
- Your HMAC key seals the audit chain
Evidence for regulators and auditors
Tamper-evident audit log
Append-only and hash-chained. Verify chain in the console shows whether any record has been changed.
Framework crosswalks
Agent decisions are tagged against the OWASP Agentic Top 10, with NIST AI RMF, ISO/IEC 42001, EU AI Act and MITRE ATLAS crosswalks.
CSV and JSON evidence files
Export audit logs as JSON or CSV, or schedule exports to S3, Azure Blob, Google Cloud Storage or BigQuery.
Frameworks and rules we map to
Mapped to means our controls and records support your own assessment. They do not make you compliant. See AI compliance for the full table.
| Framework or rule | What DeepintShield provides |
|---|---|
| AI frameworks (mapped to) | |
| OWASP LLM Top 10 | Guardrail cards for prompt injection, sensitive information disclosure and other LLM risks |
| OWASP Agentic Top 10 | Allow, Deny or Require approval on tool calls, with decisions tagged to each risk |
| NIST AI RMF | Policy enforcement, monitoring data and crosswalks on agent decisions |
| ISO/IEC 42001 | Versioned policies, role-based access and retained evidence |
| EU AI Act | Automatic decision logs and human approval steps for agent actions |
| MITRE ATLAS | RAG findings and agent decisions mapped to MITRE ATLAS |
| Laws and regulators (helps you meet) | |
| India's DPDP Act | Redaction of Aadhaar, PAN and other personal data, plus access logs |
| RBI FREE-AI framework | Policy controls, approvals for agent actions and audit evidence |
| GDPR | Data kept in your environment, personal data redacted and access logged |
| HIPAA | Patient identifiers redacted, role-based access and audit logs |
Questions from regulated teams
Does any data leave our country?
Not unless you choose it. In hybrid and self-hosted modes, no data leaves your environment. On the managed cloud, the hosting region is chosen to meet your requirements. Calls to an outside model provider go where that provider runs, so choose providers or self-hosted models that fit your rules.
Can it run without internet access?
Yes. Enterprise Self-Hosted has an air-gapped delivery option. Pair it with self-hosted models served through Ollama, vLLM or SGLang so requests stay inside your network. Read the deployment overview.
Who holds the encryption keys?
You do, in VPC and self-hosted deployments. Enterprise VPC uses keys from your own KMS, model provider keys stay on your own accounts, and you set the HMAC key that seals the audit chain.
Does using DeepintShield make us compliant?
No. No tool makes an organisation compliant. DeepintShield provides controls and evidence mapped to AI frameworks, and your legal and compliance teams decide how each rule is met. Our trust and security page explains how we handle your data.
Discuss your regulatory requirements
Tell us your sector, your rules and where the platform must run. We will show you the controls and evidence that fit.