
OWASP LLM Top 10 checklist (2025)
A practical review of the 2025 OWASP Top 10 for LLM applications: one question to check per risk and the DeepintShield control…
Meet DeepintShield at Bengaluru Tech Summit 2026, 17 to 19 November, BIEC Hall 1, booth H1A106. Book 20 minutes
Resource Center
AI security resources from DeepintShield: practical guides, checklists and templates for teams putting LLM apps and AI agents into production. Start with the OWASP LLM and Agentic Top 10 checklists, an MCP security checklist, a buyer’s guide to self-hosted AI gateways, an EU AI Act readiness guide and an architecture review pack.
Filter by type, then open a resource to read it in full.

A practical review of the 2025 OWASP Top 10 for LLM applications: one question to check per risk and the DeepintShield control…

Ten checks for AI agents, from goal hijack to rogue agents, each with the identity, authorisation or evidence control that helps.
Fourteen checks for Model Context Protocol servers and clients: connection, access, execution, content and evidence.
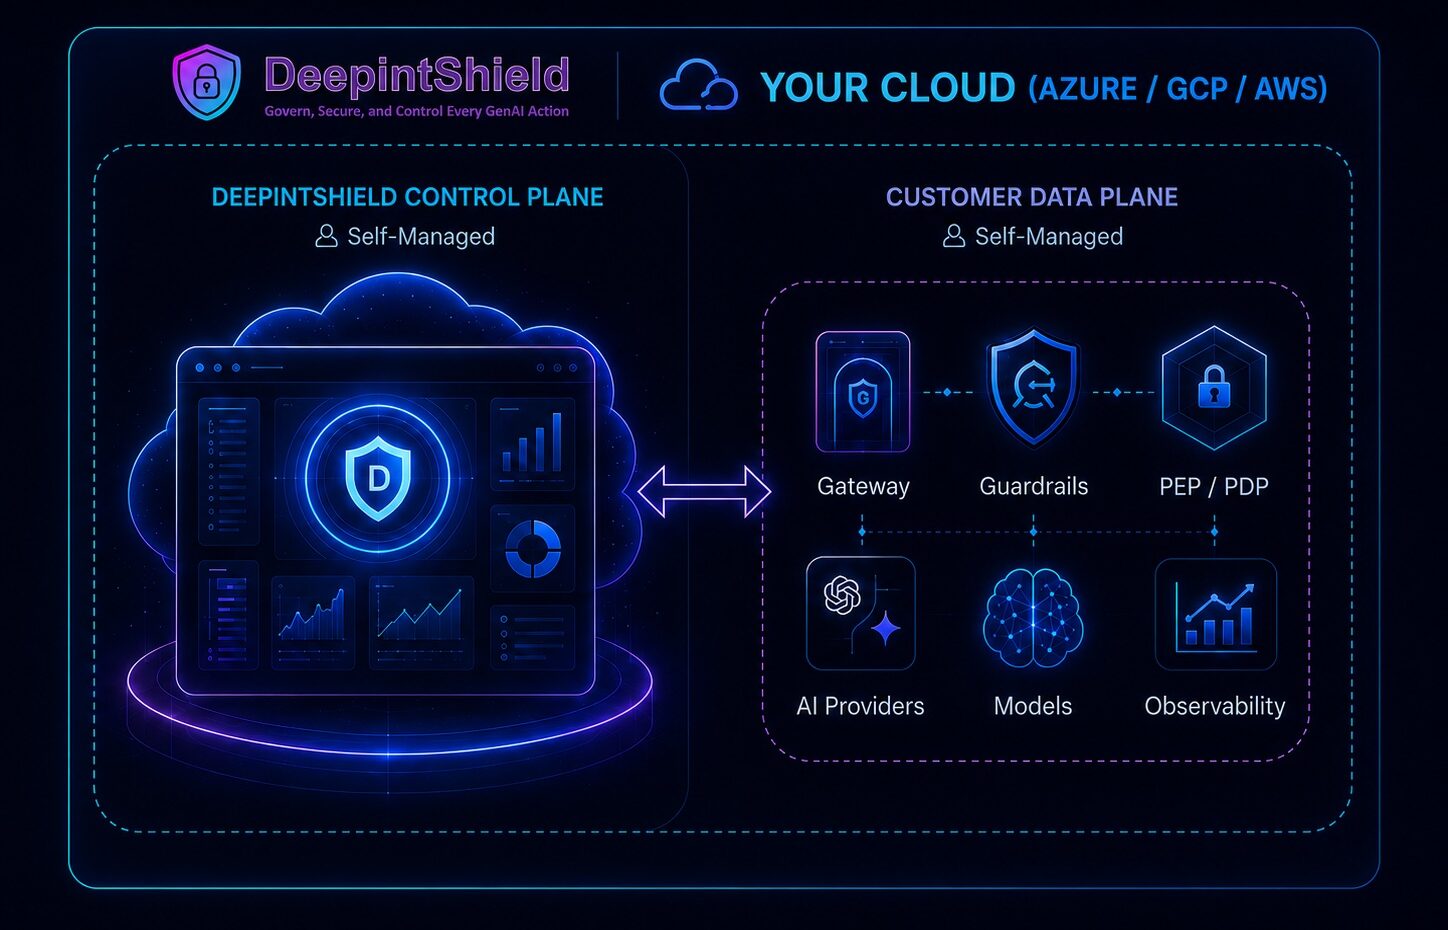
How to compare self-hosted and hybrid AI gateways: deployment models, questions to ask, what to test and who operates what.
Practical preparation steps for teams running generative AI under the EU AI Act: describe the use, assess the role, map controls and…
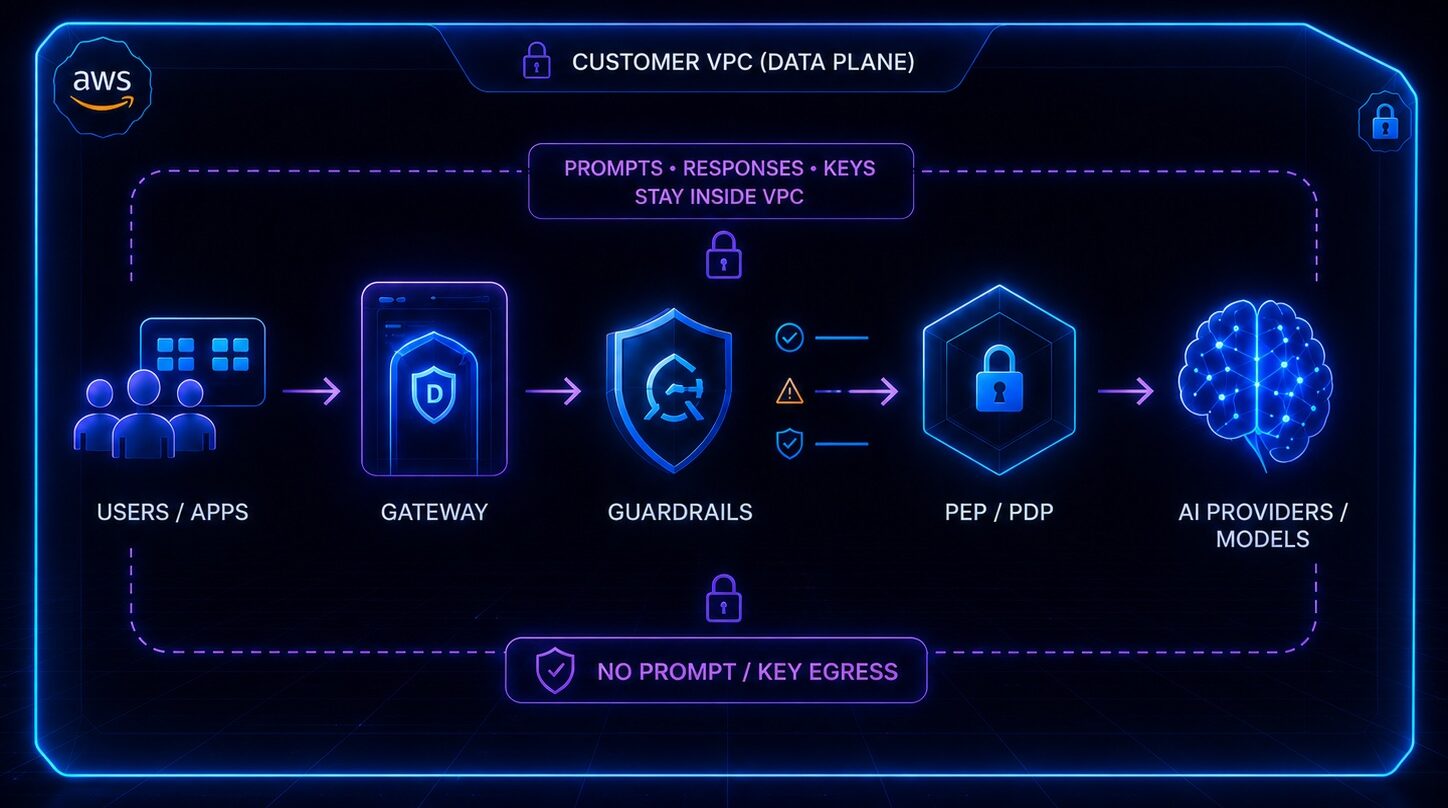
What to bring to an architecture review board for DeepintShield: diagrams, data flows per deployment mode, latency, identity and evidence.
Every resource is written with one of three readers in mind.
Use the OWASP checklists to find gaps in prompts, retrieval, agent actions and MCP servers before an auditor does.
Use the buyer’s guide and the architecture review pack to decide where the gateway runs and who operates it.
Use the EU AI Act readiness guide to plan record-keeping and evidence for each AI use case.
Each resource matches a part of the DeepintShield platform, so you can move from a checklist item to the control that covers it. Every checklist and guide opens as a full page you can read and print, with no sign-up. For the regulatory side, see how controls map to frameworks on the AI compliance page, or go straight to the documentation.

Prefer a quick self-check? The free AI Runtime Risk Scan asks twelve questions and scores six areas in about two minutes.

Five Stages of LLM Guardrails: What Each One Checks An AI workflow can receive a question, retrieve a document, call a tool…
DeepintShield team · · 5 min read

OWASP Agentic ASI Top 10: Risks and Practical Controls The OWASP Agentic ASI Top 10 (2026) is a framework that lists the…
DeepintShield team · · 6 min read

What Is an MCP Gateway? Tool Access and Policy Checks An MCP gateway gives an application a common route to connected Model…
DeepintShield team · · 5 min read
Short articles on guardrails, agent security, MCP, cost and compliance, written for engineers and security leads.
Read the blog
Straight answers on deployment, data handling, plans and pricing, and how the platform fits your stack.
Read the FAQ
Setup guides, the API reference and the Python SDK 3.2.3 reference, with limits and plan gating stated.
Read the Docs
Book a 20-minute call and an engineer will walk through it against your own stack.