
Solutions · AI compliance
AI compliance: tamper-evident evidence for your AI decisions
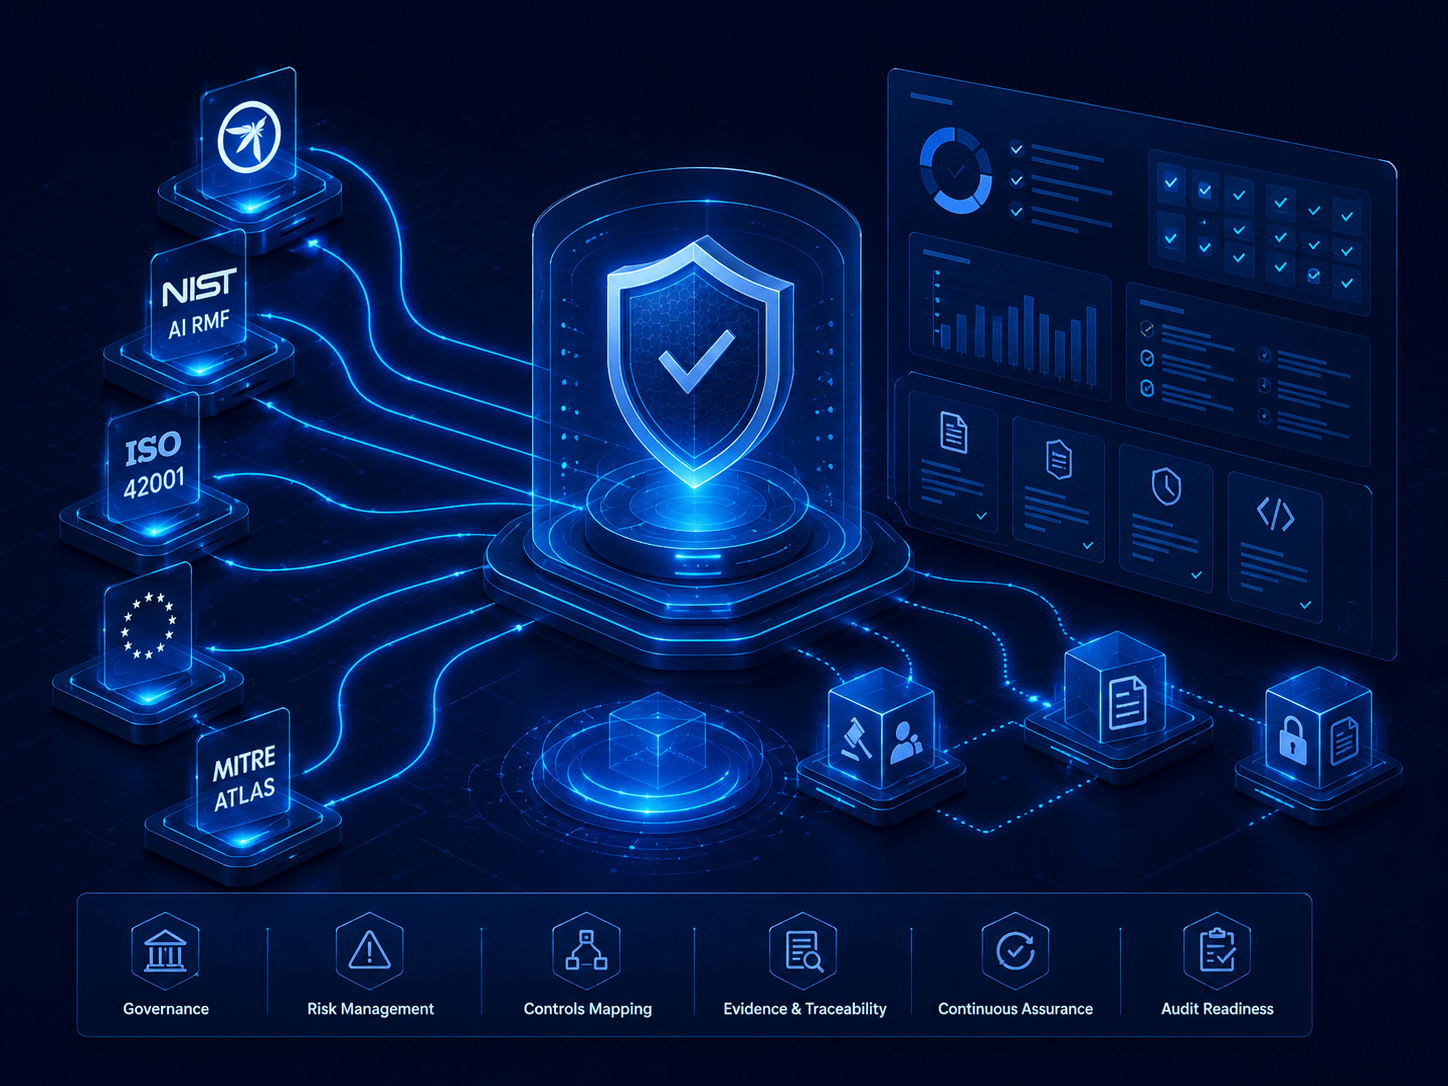
AI compliance means being able to show a regulator or auditor what your AI systems did and which rules applied. DeepintShield records runtime and admin decisions in a hash-chained audit log, maps its controls to the main AI frameworks and exports the evidence, so an audit request becomes an export, not a project.
- Hash-chained, append-only ledger
- Mapped to six AI frameworks
- JSON and CSV evidence exports
Why AI compliance is hard
New AI-specific frameworks
The EU AI Act, ISO/IEC 42001 and NIST AI RMF add expectations that general security controls do not cover.
Records nobody can verify
Plain application logs can be edited without trace, so an auditor cannot tell whether a record was changed.
Agent supply-chain risk
Agents call tools and MCP servers whose definitions can change without anyone noticing.
Data-residency exposure
Prompts with personal data reach models in other countries, often with no record of where they went.
Frameworks DeepintShield maps to
What each framework expects, and the controls and records DeepintShield provides. Mapped to means they support your own assessment; they do not make you compliant.
| Framework | What it asks for | What DeepintShield provides |
|---|---|---|
| AI frameworks (mapped to) | ||
| OWASP LLM Top 10 (2025) | Controls for the main risks in LLM applications, such as prompt injection, sensitive information disclosure and excessive agency. | OWASP LLM Top-10 guardrail cards on every plan; input, output and RAG checks; 460+ detection patterns. |
| OWASP Agentic Top 10 | Controls for agent risks such as goal hijacking, tool misuse, identity abuse and rogue agents. | Agentic guardrail cards; Allow, Deny or Require approval on governed tool calls; decisions tagged to each risk. |
| NIST AI RMF | A voluntary way to govern, map, measure and manage AI risk across a system's life. | Policy enforcement, monitoring metrics and NIST AI RMF crosswalks on agent decisions. |
| ISO/IEC 42001 | An AI management system: policies, risk treatment, controls, monitoring and records, improved over time. | Versioned policies, role-based access, retained evidence (730 days by default) and ISO 42001 crosswalks. |
| EU AI Act | Risk-based duties that depend on your role and use case; high-risk systems need record-keeping, human oversight and cybersecurity, among others. | Automatic decision logs, human approval for agent actions and EU AI Act crosswalks on decisions. |
| MITRE ATLAS | A knowledge base of adversary tactics and techniques against AI systems, used for threat modelling. | RAG findings and agent decisions mapped to MITRE ATLAS. |
| Security and privacy audits (audit logging supports evidence for) | ||
| SOC 2 and ISO/IEC 27001 | Evidence that security controls such as access control, change management and logging work over time. | Audit logging supports evidence for these audits: authentication, configuration and security events in CADF format, exported as JSON or CSV. |
Audit logging also supports GDPR and HIPAA evidence. Confirm how each mapping applies to your system with your assessor.
What you get
The evidence comes from the same platform that enforces your runtime guardrails and agent controls, not from a separate reporting tool.
Hash-chained audit log
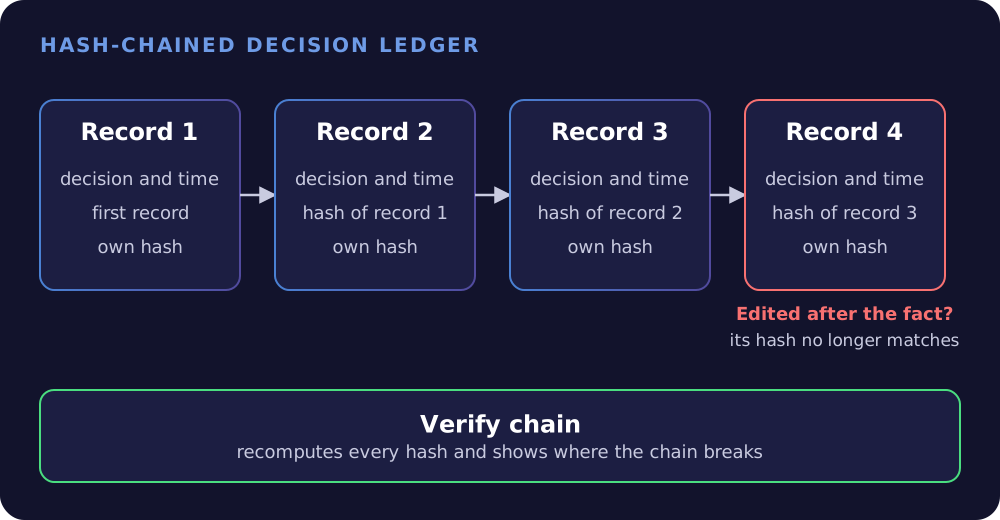
Workspace-scoped, append-only and hash-chained. Each agent decision is written before the call proceeds.
Framework crosswalks
Agent decisions are classified against the OWASP Agentic Top 10, with NIST AI RMF, ISO 42001, EU AI Act and MITRE ATLAS crosswalks.
AI Bill of Materials
Export a JSON inventory of governed tool contracts, signed when a signing key is configured. Business and above.
OWASP guardrail cards
Ready-made OWASP LLM Top 10 and Agentic cards turn framework risks into enforced policies.
CSV and JSON exports
Audit logs as JSON or CSV, decisions as CSV, and scheduled log exports to S3, BigQuery or Snowflake.
Self-hosted with no data egress
In hybrid and self-hosted modes, no data leaves your environment, and that includes your evidence.
From decision to audit evidence in one step
When an agent asks to call a tool, the decision is written to the ledger before the call runs. If it cannot be recorded, the call does not proceed. Each record holds the hash of the one before, so a changed record breaks the chain.
Auditors use Verify chain in the console, or the verify API, to recompute it. Production deployments refuse to start without an HMAC key, so a database writer cannot quietly rebuild the chain. See Observability & Audit for traces and exports.
- Verify chain in the console and through the API
- Evidence kept for 730 days by default
- Log exports, OpenTelemetry, Prometheus and durable webhooks
AI compliance questions
Does DeepintShield make us compliant?
No. No tool makes a company compliant. DeepintShield provides controls and evidence mapped to AI frameworks, and your compliance team and assessors decide whether your system meets each requirement.
What is an AI Bill of Materials?
An AIBOM is an inventory of the AI components a system uses. In DeepintShield, Export AIBOM produces a JSON inventory of governed tool contracts, signed when a signing key is configured and marked unsigned otherwise. Read the Agentic Security docs.
Which frameworks are covered?
Six AI frameworks: OWASP LLM Top 10, OWASP Agentic Top 10, NIST AI RMF, ISO/IEC 42001, the EU AI Act and MITRE ATLAS. Audit logging also supports evidence for SOC 2, ISO 27001, GDPR and HIPAA reviews.
Can auditors verify the log themselves?
Yes, with the access you grant. Verify chain in the console recomputes the hash chain, and the same check runs through an API. A Viewer role lets an auditor read without changing anything. Our trust and security page covers how we protect the platform itself.
How long is evidence kept?
730 days by default for agent decisions. You can change the retention period, and export records to your own storage to keep them longer.
Related pages
Governance
Virtual keys, budgets, roles and SSO that decide who may use which model.
See Governance
Observability & Audit
Traces, metrics, exports and the tamper-evident log that your audit evidence comes from.
See Observability & Audit
Regulated industries
Banking, government, healthcare and global capability centres, with the rules each one faces.
See industries
Make AI audits an export, not a project
Start free on the Developer plan, or book a demo to see evidence exports on your own stack.