
Solutions
AI security solutions for every team that runs AI in production
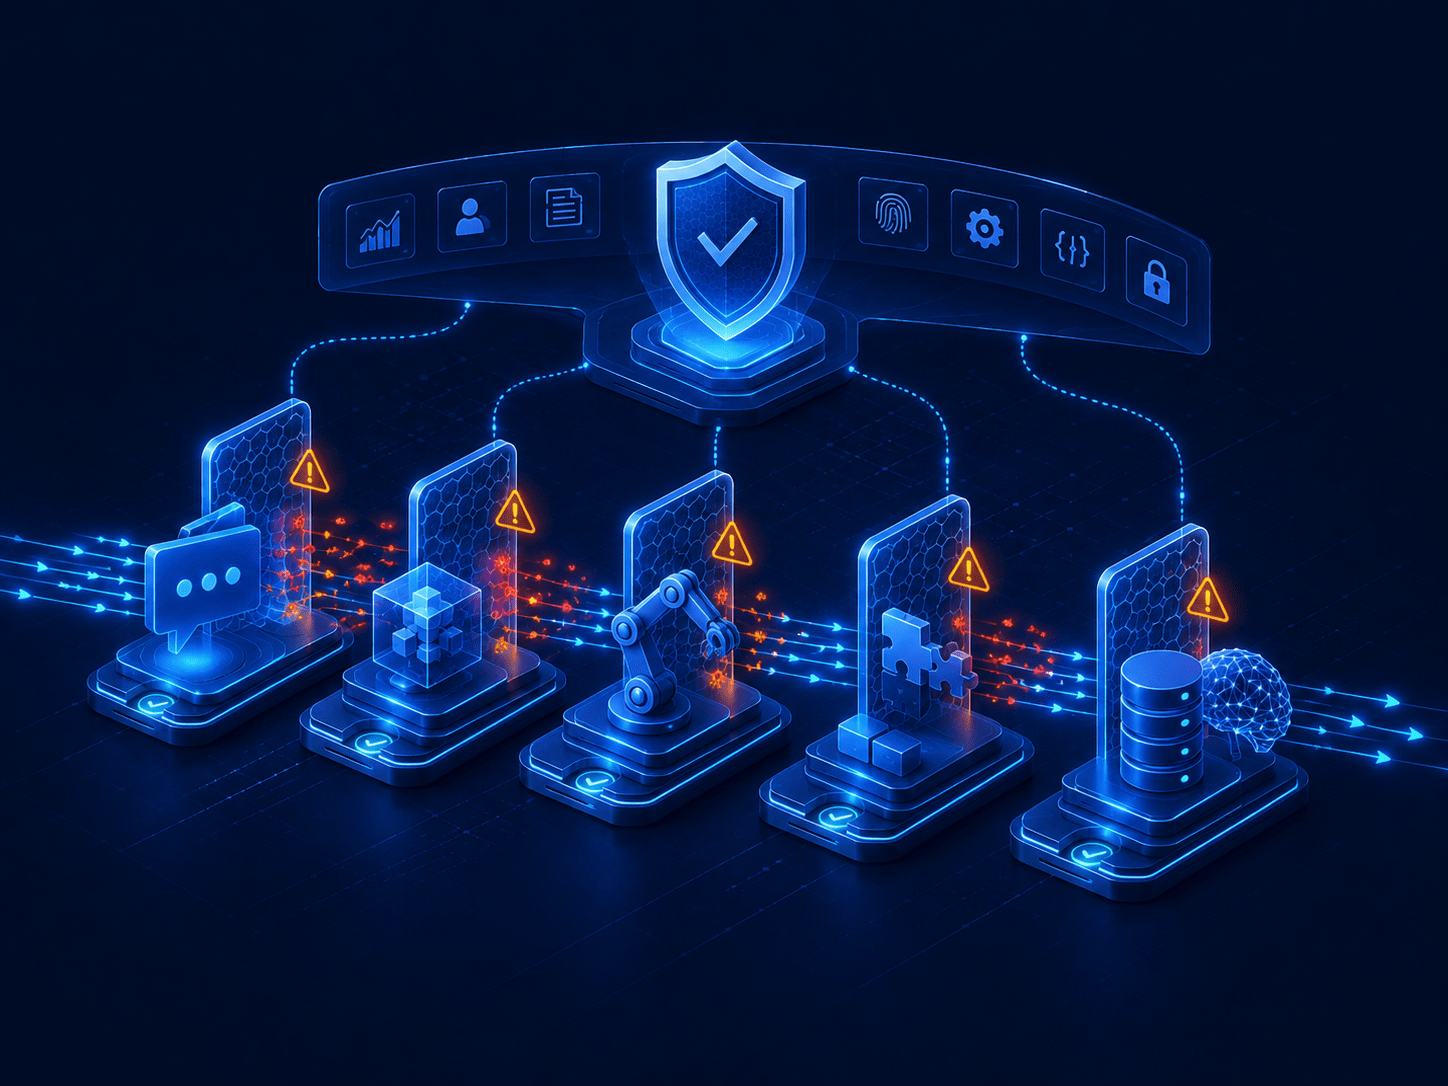
AI security solutions put controls around the models, agents and data your teams already use. DeepintShield offers them by need, by industry and by deployment, so a CISO, a compliance lead and a platform engineer can each start from the page that answers their question, then share one platform.
- One gateway for models, agents and MCP tools
- Guardrails at five enforcement stages
- Managed, hybrid or self-hosted
AI security solutions by need
Start from the question you have to answer this quarter, whether it comes from the board, an auditor or your own engineers.
Enterprise AI
For CISOs and review boards: where data goes, what agents may do and how to prove it.
Enterprise AI security
AI compliance
For compliance leads: a hash-chained audit log and controls mapped to six AI frameworks.
AI compliance evidence
Use cases
For builders: secure a copilot, stop personal data leaks, govern agents and set team budgets.
Browse use cases
By industry
Regulated sectors need data kept in country, personal data redacted and evidence ready for review. Start with the regulated industries overview, or pick your sector.
Banking and financial services
RBI FREE-AI and India’s DPDP Act: customer data redacted before any model, with audit evidence.
AI security for banks
Government and public sector
Sovereign deployment: self-hosted or air-gapped, with keys and audit records under your control.
Sovereign AI security
Healthcare
Medical record numbers and patient IDs redacted inline, access by role and an audit record.
AI security for healthcare
Global capability centres
One gateway for many teams, parent-company policies applied centrally and a budget per team.
AI governance for GCCs
By deployment
Choose who runs what. Every option uses the same platform and policies. The deployment overview compares them, and the deployment guides cover setup.
Fully managed cloud
We run the control plane and data plane. The hosting region is chosen to meet your requirements, with zero retention available.
Managed cloud
Hybrid cloud
Your data plane runs in your VPC. We run the control plane over one outbound-only mutual-TLS link.
Hybrid cloud
Self-hosted
Everything runs in your environment, with an air-gapped delivery option on Enterprise Self-Hosted.
Self-hosted
Where to start
Match the problem in front of you to the page that answers it.
| If you need to | Start here |
|---|---|
| Answer your review board on data, agents and audit | Enterprise AI |
| Give auditors evidence mapped to AI frameworks | AI compliance |
| Stop staff sending personal data to AI tools | Runtime Guardrails & PII |
| Control what agents and MCP tools may do | Agentic Security and MCP Gateway |
| Give many teams model access, with budgets | Governance |
| Keep data in country, or run air-gapped | Self-hosted deployment |
| Check retrieved documents before the model reads them | RAG Security |
| Keep apps answering when a provider fails | AI Gateway |
| Cut LLM spend without rewriting apps | Cost Optimization |
One platform under every solution
Each solution uses the same DeepintShield platform: one AI gateway in front of 29 built-in model providers, guardrails at five checkpoints, and a decision for every governed agent action. The request path shows where each check runs. Policies, keys and logs are shared, so security, compliance and engineering teams work from the same records instead of separate tools.
- Guardrails at Input, RAG, Action, MCP and Output
- Allow, Deny or Require approval for agent tool calls
- Budgets, virtual keys and role-based access
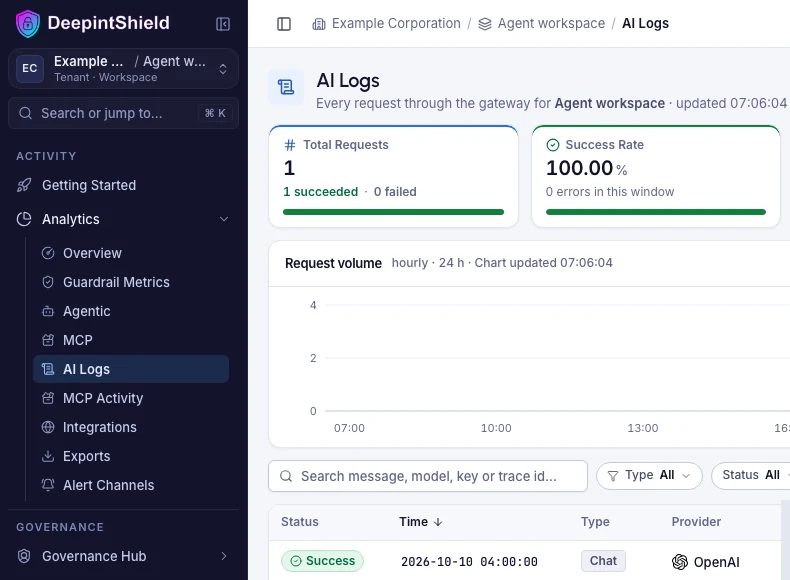
- A hash-chained audit log you can verify
How to get started
You can move from a free trial to enforced policies in four steps.
1. Start free
Try the gateway on the Developer plan: free, with 50,000 requests a month and your own model keys.
2. See it on your stack
Book a 20-minute call with an engineer, on your own stack and use case.
3. Run a pilot
Run a 30-day pilot on Cloud Business, or validate a VPC or sovereign deployment in your cloud.
4. Roll out in stages
Move from monitor to shadow, canary and enforce as findings settle on your real traffic.
Not sure which solution fits?
Tell us what you are building and we will show you how to secure it.