
AI Logs
Hash-Chained Audit Logs: Tamper-Evident Compliance for AI Decisions
A hash-chained audit log records every decision in a way that makes tampering detectable: each entry includes a cryptographic hash of the…
Meet DeepintShield at Bengaluru Tech Summit 2026, 17 to 19 November, BIEC Hall 1, booth H1A106. Book 20 minutes
Banking · Detects PAN, Aadhaar, IBAN and card numbers
AI security for banks means using AI in line with the RBI FREE-AI framework and India’s DPDP Act without exposing customer data or losing the audit trail. DeepintShield redacts identifiers such as PAN, Aadhaar and card numbers before a prompt reaches any model, decides what agents may do and keeps tamper-evident evidence for auditors.
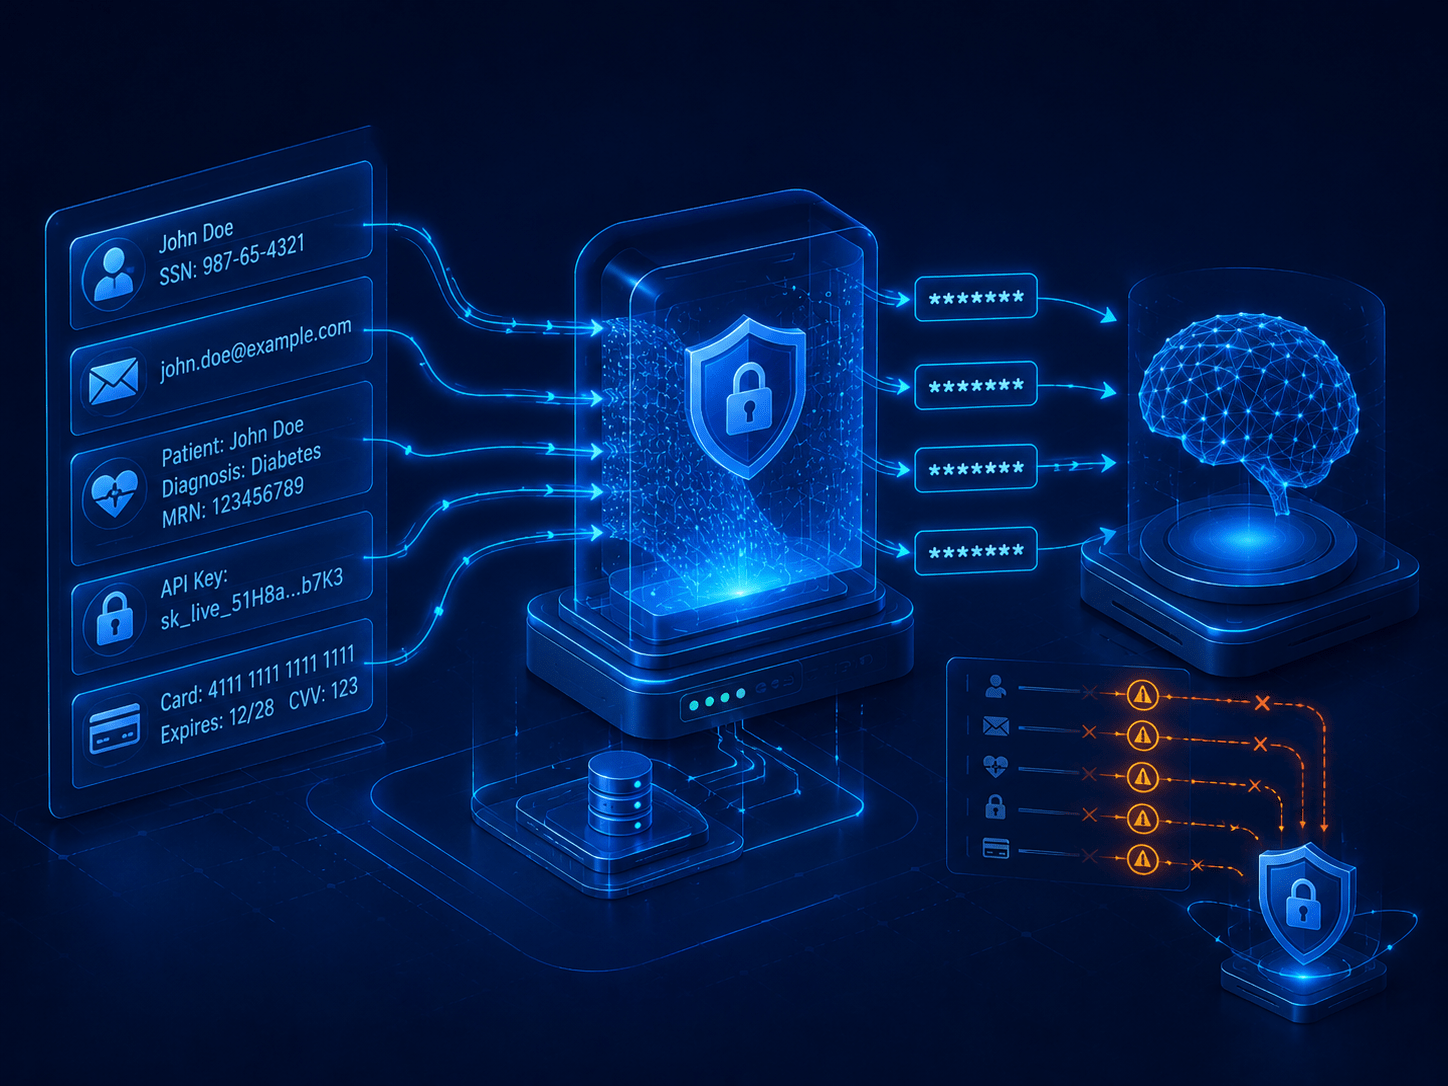
Staff paste account details, PAN or Aadhaar numbers into AI tools, and the data travels to an outside model.
An assistant that can read accounts or raise requests may act beyond its task if nothing checks each call.
Supervisors ask which model saw what data and who approved an action. Scattered logs cannot show it.
Switch on presets that already exist in the product, then tune them to your own data.
Guardrails for prompt injection, jailbreaks and sensitive information disclosure, available on every plan.
Presets for goal hijacking, tool misuse, identity abuse and rogue agent behaviour.
Finds PAN, Aadhaar, IBAN, card and passport numbers, with a BFSI domain pack, and redacts them before the model.
Finds API keys, private keys, tokens and auth headers, and blocks or redacts them before a model sees them.
Bring a real banking workflow. We will run it through DeepintShield with you.
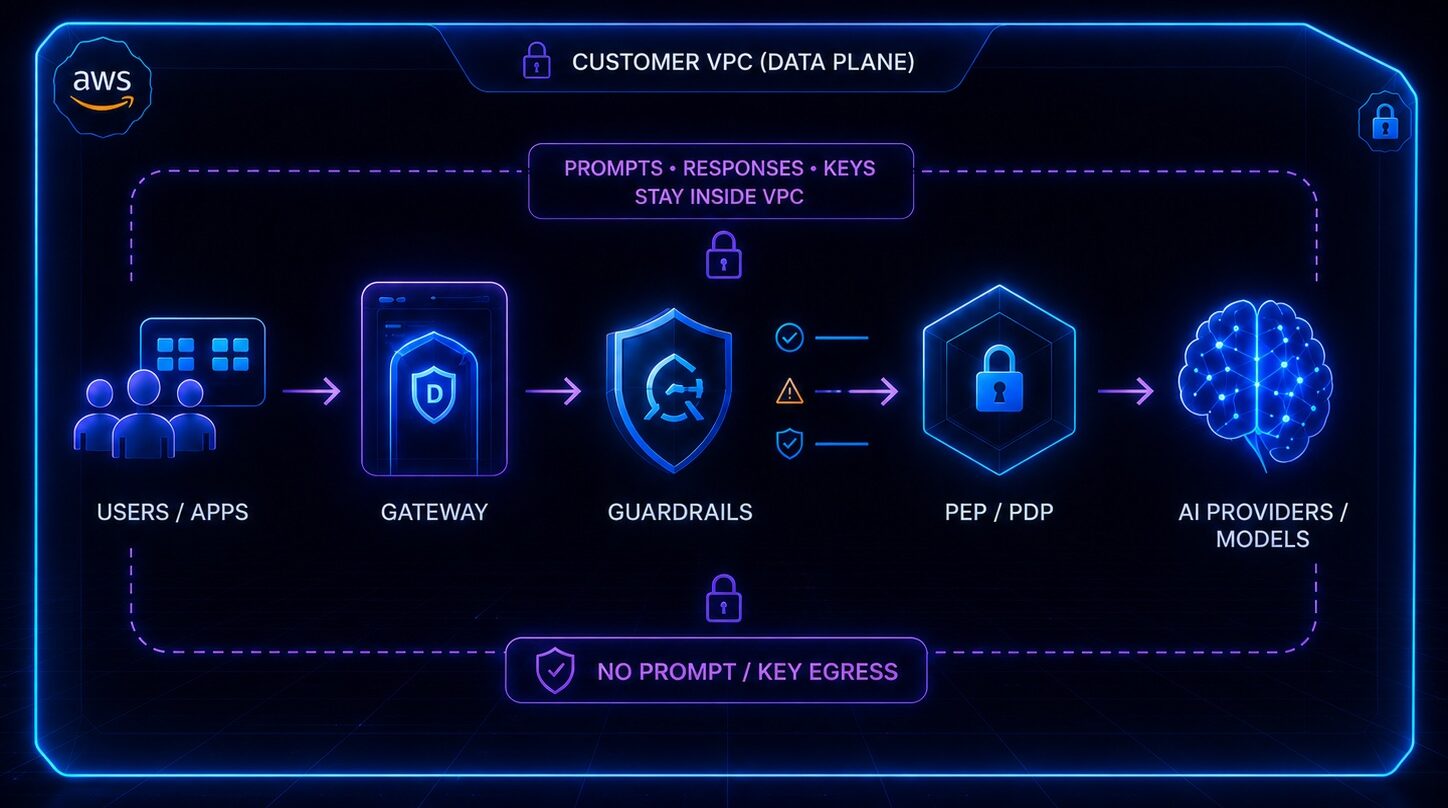
Run the data plane in your own VPC or self-host the whole platform. In hybrid and self-hosted modes, no data leaves your environment. On the managed cloud, the hosting region is chosen to meet your requirements.
PII redaction rewrites prompts, responses, streaming output, RAG chunks and tool calls. Detection runs inside your deployment, and a redaction that cannot be applied safely becomes a block.
Every governed tool call gets Allow, Deny or Require approval. Neither the requester nor the agent's owner can approve. Agentic Security is on Business and above.
Agent decisions are written to a hash-chained ledger before the call runs, kept for 730 days by default and exported as CSV.
Set budgets and rate limits per team and virtual key, and use 12 cost techniques. Semantic caching saves up to 60% on repetitive workloads; results depend on the workload.
If a provider errors or times out, fallbacks try the next provider or model in your order, so customer-facing apps keep answering.
29
built-in model providers
plus custom OpenAI-compatible endpoints
460+
detection patterns
462 entries in 102 preset families
5
enforcement stages
Input, RAG, Action, MCP and Output
730 days
default evidence retention
for the agent decision ledger
Product facts from the DeepintShield docs, not customer results. Pattern counts are configuration entries, not a measure of accuracy.
Redact PAN, Aadhaar and card numbers before any prompt reaches a model.
Read the use case
Give supervisors a verifiable record of what each AI system and agent did.
Read the use case
Hold high-risk agent actions until a second person approves them.
Read the use case
Mapped to
Helps you meet
DeepintShield provides controls and evidence; it does not make a bank compliant. See AI compliance for the framework table, or other regulated industries.
It provides controls and evidence that support it. The Reserve Bank of India's FREE-AI framework sets out how regulated entities should adopt AI responsibly, with governance, risk controls, monitoring and audit. DeepintShield enforces policies on every request through the gateway, holds risky agent actions for approval and keeps a hash-chained audit trail.
It helps you meet the Act's security duties, but it does not make you compliant. The Digital Personal Data Protection Act, 2023 expects organisations to protect the personal data they process with reasonable security safeguards. DeepintShield redacts personal data before it reaches a model and logs who accessed what.
Yes. Enterprise VPC runs the data plane in your Kubernetes cluster, and no prompt, response, key or audit data leaves your VPC. Enterprise Self-Hosted runs everything in your environment. See hybrid deployment.
Common financial and identity data. The detector list covers India PAN, Aadhaar, IBAN, card numbers, passport numbers, e-mail and phone, plus a BFSI domain pack. Test it on samples of your own data. Read the PII redaction docs.
Yes. Bring your own provider keys with no token markup, choose from 29 built-in model providers, or connect self-hosted models through Ollama, vLLM or any OpenAI-compatible endpoint.
A hash-chained audit log records every decision in a way that makes tampering detectable: each entry includes a cryptographic hash of the…
DeepintShield team · · 4 min read

Self-Hosted vs SaaS AI Security: Compare Data Flows Choosing where to run an AI security gateway is also a choice about who…
DeepintShield team · · 5 min read
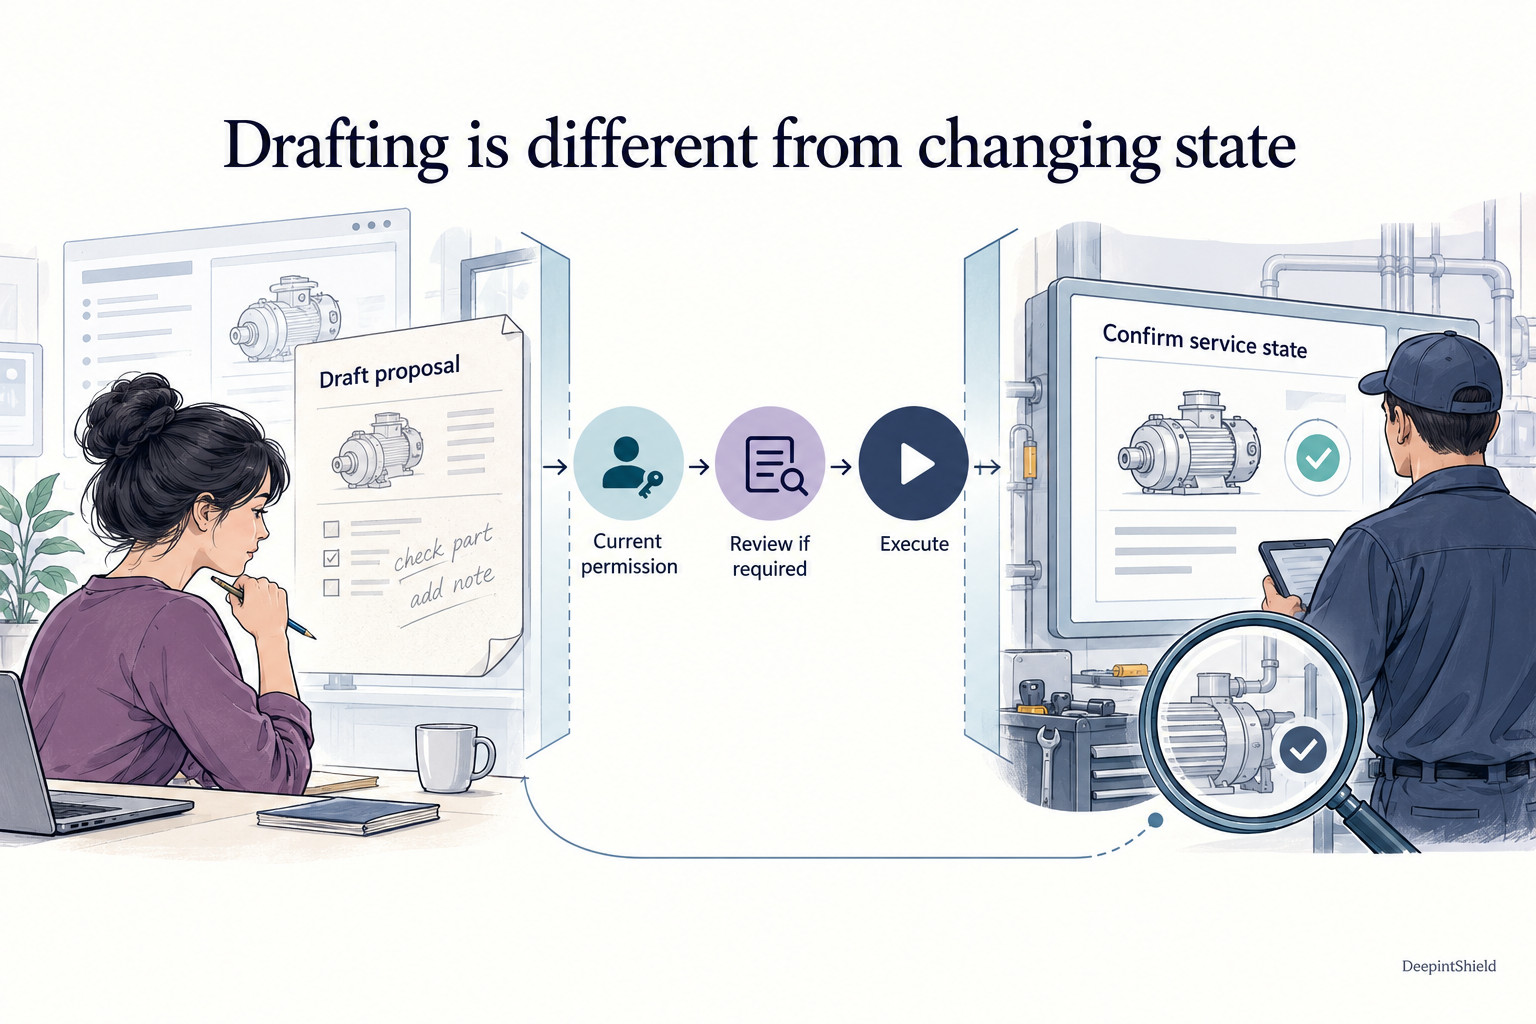
Agentic Security: Why AI Actions Need Clear Controls A sales assistant that reads product details has a different responsibility from one that…
DeepintShield team · · 5 min read
Show us the workflow and the rules it must meet. We will map the controls and evidence to it.