

AI Logs
Five Stages of LLM Guardrails: What Each One Checks
Five Stages of LLM Guardrails: What Each One Checks An AI workflow can receive a question, retrieve a document, call a tool…
Meet DeepintShield at Bengaluru Tech Summit 2026, 17 to 19 November, BIEC Hall 1, booth H1A106. Book 20 minutes
Healthcare · MRN and patient ID redaction
AI security for healthcare means clinicians and staff can use AI without patient data reaching an outside model or losing track of who saw what. DeepintShield redacts identifiers such as medical record numbers inline, limits access by role and keeps an audit record that helps you meet HIPAA and similar rules.
Clinicians paste notes with record numbers and contact details into AI tools that send them to an outside model.
Without role-based access, anyone with a console login can change policies or read logs that hold sensitive data.
When a privacy officer asks what an AI system saw and returned, scattered logs give no clear answer.
Switch on presets that already exist in the product, then tune them to your own data.
Detects MRN and patient IDs, plus SSN, e-mail and phone numbers, with a healthcare domain pack, and redacts them inline.
Guardrails for prompt injection, jailbreaks and sensitive information disclosure, available on every plan.
Presets for goal hijacking, tool misuse, identity abuse and rogue agent behaviour.
Finds API keys, private keys, tokens and auth headers, and blocks or redacts them before a model sees them.
Bring a real clinical or administrative workflow, with test data. We will run it through DeepintShield with you.
MRN, patient ID, SSN, phone and e-mail are rewritten in prompts, responses, streaming output, RAG chunks and tool calls. Detection runs inside your deployment.
Admin, Viewer and custom roles cover 14 resource types, including audit logs and guardrail settings. Staff sign in through your OIDC provider, with MFA.
Audit logs record authentication, configuration, data-access and security events in a hash-chained format you can verify.
In hybrid and self-hosted modes, no data leaves your environment. You can also turn off content logging so prompts and responses are not stored.
Hold an agent's write to a record system until a person approves it. Approvers cannot be the requester. Business and above.
Hallucination Defense scores answers with five detectors and an overall risk score, on Business and above.
460+
detection patterns
462 entries in 102 preset families
5
enforcement stages
Input, RAG, Action, MCP and Output
730 days
default evidence retention
for the agent decision ledger
29
built-in model providers
plus custom OpenAI-compatible endpoints
Product facts from the DeepintShield docs, not customer results. Pattern counts are configuration entries, not a measure of accuracy.
Redact medical record numbers and patient IDs before any prompt reaches a model.
Read the use case
Give staff an AI assistant with redaction, role-based access and an audit record.
Read the use case
Show a privacy or compliance review what each AI system and agent did.
Read the use case
Mapped to
Helps you meet
Audit logging supports evidence for HIPAA, GDPR, SOC 2 and ISO 27001 reviews. DeepintShield does not make you compliant. See AI compliance or other regulated industries.
No. It helps you meet HIPAA; it does not make you compliant. The HIPAA Security Rule asks for safeguards such as access controls and audit controls for electronic protected health information. DeepintShield provides redaction, role-based access and audit logs that support that work, and your compliance team decides how each requirement is met.
Medical record numbers and patient IDs, plus SSN, phone, e-mail, passport and the other listed identifiers, with a healthcare domain pack. Test the detectors on samples of your own data. Read the PII redaction docs.
Not image content. Image checks cover metadata only, with no OCR, and PDF text is checked within documented size limits. Keep scanned records out of prompts, or extract the text first.
Where you choose. In hybrid and self-hosted modes, no data leaves your environment. On the managed cloud, the hosting region is chosen to meet your requirements.
Only the roles you allow. Role-based access controls who can view or download audit logs, and you can turn off content logging so prompts and responses are not stored.
Five Stages of LLM Guardrails: What Each One Checks An AI workflow can receive a question, retrieve a document, call a tool…
DeepintShield team · · 5 min read
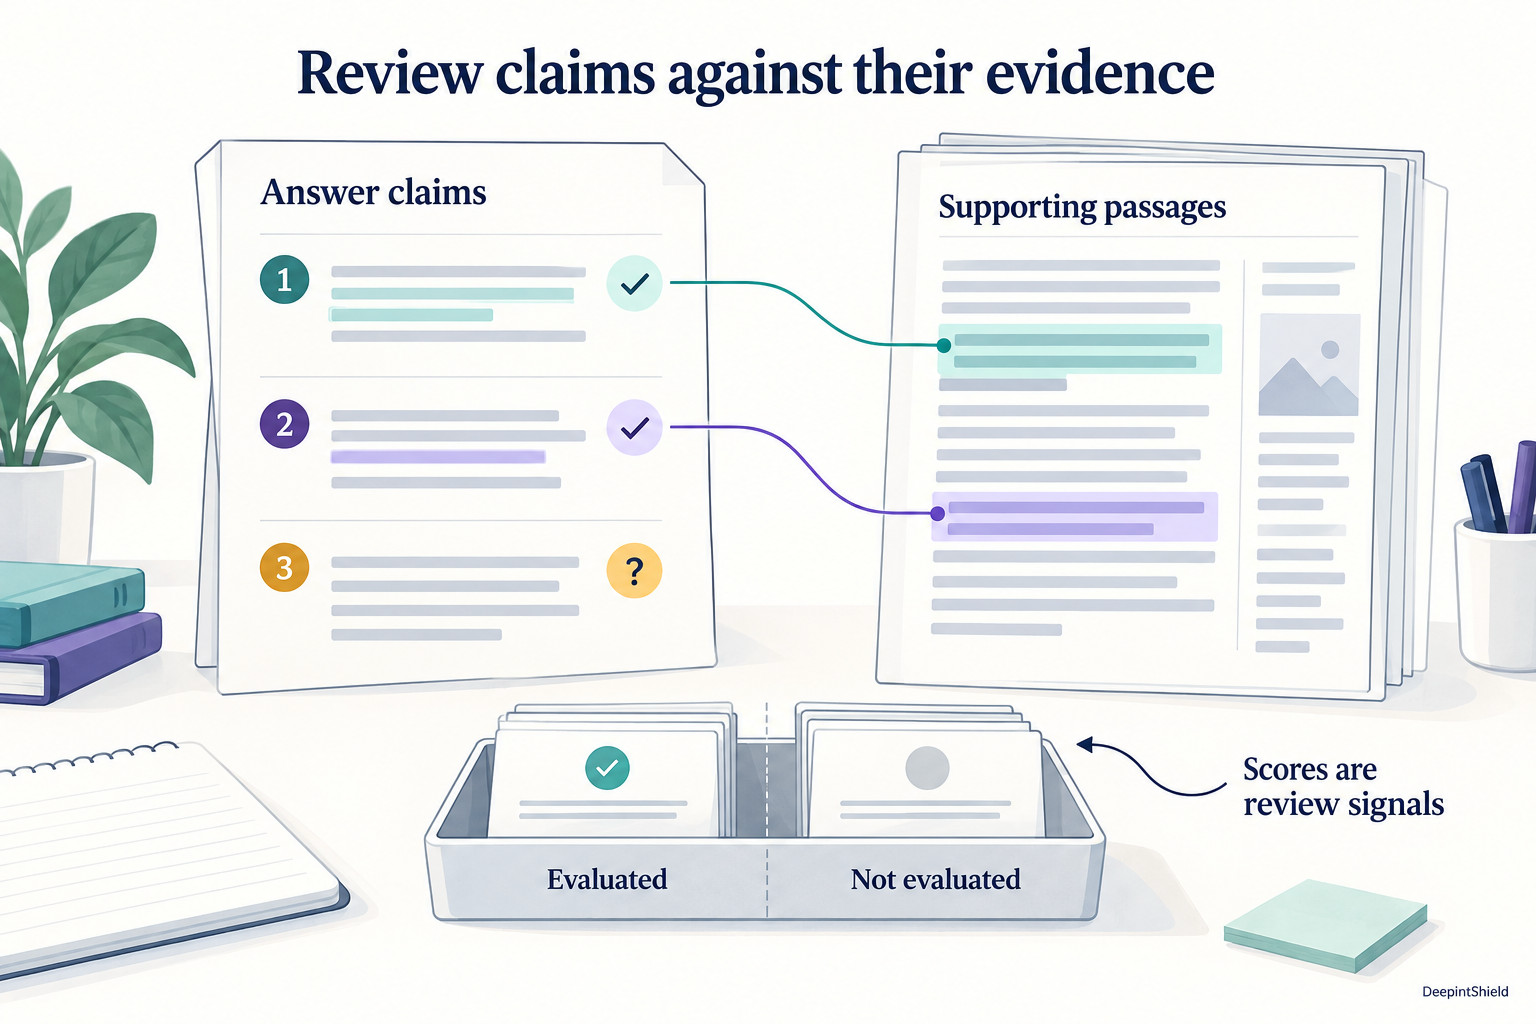
LLM Hallucination Checks: Grounding and Answer Quality A useful AI answer should address the question and show where its factual claims come…
DeepintShield team · · 5 min read
A hash-chained audit log records every decision in a way that makes tampering detectable: each entry includes a cryptographic hash of the…
DeepintShield team · · 4 min read
Show us the workflow and the rules it must meet. We will map the controls and evidence to it.