
AI Logs
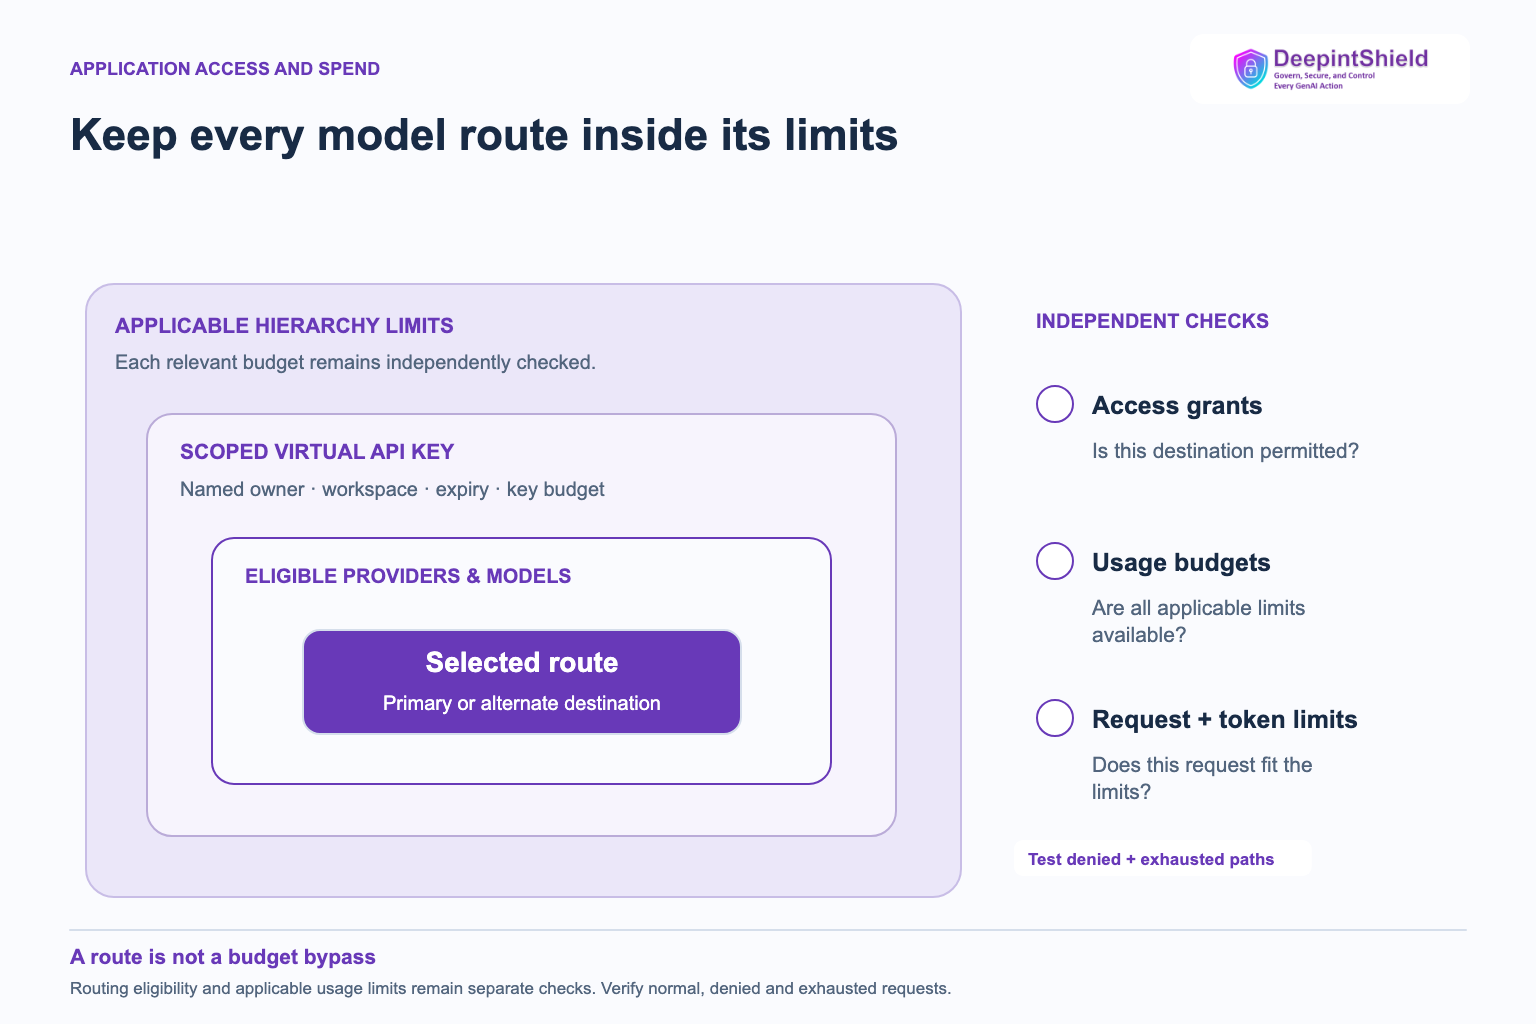
Virtual API Keys: Budgets, Model Access and Routing Boundaries
Virtual API Keys: Budgets, Model Access and Routing Boundaries An application credential should express which AI services the application can use and…
Meet DeepintShield at Bengaluru Tech Summit 2026, 17 to 19 November, BIEC Hall 1, booth H1A106. Book 20 minutes
Global capability centres · One gateway, many teams
AI governance for GCCs means every team in a global capability centre uses AI through the same controls its parent company sets. DeepintShield gives you one gateway for all teams, applies group policies centrally, sets a budget for each team and keeps one audit record across them.
Dozens of teams sign up for different AI services, each with its own keys, rules and gaps.
Model costs grow across projects with no budget per team and no clear chargeback to the parent company.
The parent company sets AI rules, but each team enforces them differently, or not at all.
Switch on presets that already exist in the product once, and apply them to every team.
Guardrails for prompt injection, jailbreaks and sensitive information disclosure, available on every plan.
Presets for goal hijacking, tool misuse, identity abuse and rogue agent behaviour.
Finds e-mail, phone, PAN, Aadhaar, IBAN and card numbers, and redacts them before the model.
Stops API keys, private keys, tokens and auth headers from engineering teams reaching a model.
Bring two or three teams’ workflows. We will show how one gateway governs them all.
Teams reach 29 built-in model providers through one OpenAI-compatible API, each with its own virtual key and the models it may use. See the AI gateway.
Define guardrail policies once and bind them to each team's virtual keys. Policies are versioned, so every change can be reviewed.
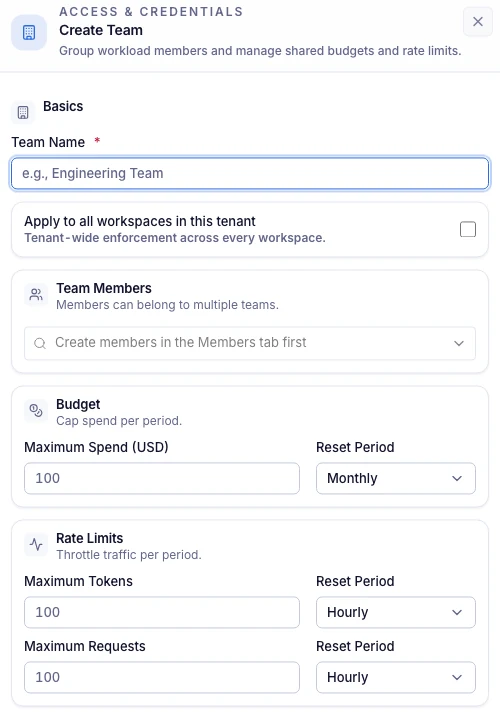
Set budgets and rate limits at customer, team, virtual-key and provider level. Every level must pass, and over-budget providers drop out of routing. Teams need Cloud Team or above.
Request logs, guardrail findings and the agent decision ledger sit in one workspace, and export to the parent company's SIEM or data warehouse.
SSO over OIDC with Microsoft Entra ID or Okta, SCIM sync with Entra ID routed by e-mail domain, and role-based access.
Use 12 cost techniques. Semantic caching saves up to 60% on repetitive workloads; results depend on the workload.
29
built-in model providers
plus custom OpenAI-compatible endpoints
4
budget levels
customer, team, virtual key and provider
12
cost techniques
savings depend on the workload
730 days
default evidence retention
for the agent decision ledger
Product facts from the DeepintShield docs, not customer results.
One gateway, one set of policies and a virtual key for each team.
Read the use case
Cap spend and rate limits per team, and report cost back to the parent company.
Read the use case
Roll out an AI assistant across teams with redaction, access control and an audit record.
Read the use case
Mapped to
Product facts
Audit logging also supports evidence for the SOC 2 and ISO 27001 reviews a parent company runs. See AI compliance or other regulated industries.
A centre that a multinational runs for its own technology, operations or research work. Many are based in India and serve business units worldwide, so they run AI for many teams under the parent company's rules.
Yes. Budgets and rate limits apply at customer, team, virtual-key and provider level, with reset periods from a minute to a month. Teams and customers are on Cloud Team and above. Read the budgets docs.
Through the gateway. Guardrail policies are versioned and bound to virtual keys, so each team's traffic is checked by the same rules. Required headers can also force a cost-centre tag on every request. See Governance.
Yes. All teams in a workspace share the same logs and audit trail, and scheduled log exports send them to S3, BigQuery, Snowflake or Azure Blob for group reporting.
It depends on the parent company's data rules. Cloud Business suits several teams and agents, Enterprise VPC puts the data plane in your cloud, and Enterprise Self-Hosted keeps everything in your environment. Compare plans and prices.
Virtual API Keys: Budgets, Model Access and Routing Boundaries An application credential should express which AI services the application can use and…
DeepintShield team · · 9 min read
Multi-Tenant LLM Platforms: Workspace Access Boundaries A shared LLM platform becomes easier to operate when teams can reuse infrastructure while keeping their…
DeepintShield team · · 5 min read
LLM Cost Optimization: 12 Ways to Reduce Wasted Work LLM cost optimization starts by finding wasted work: repeated requests, unnecessary context, unsuitable…
DeepintShield team · · 4 min read
Tell us how many teams use AI and which group policies apply. We will show you one gateway that governs them.