
Secure an internal AI copilot
Give an internal copilot its own Virtual Key, guardrails on prompts and answers, model and budget limits, and a full record of use.
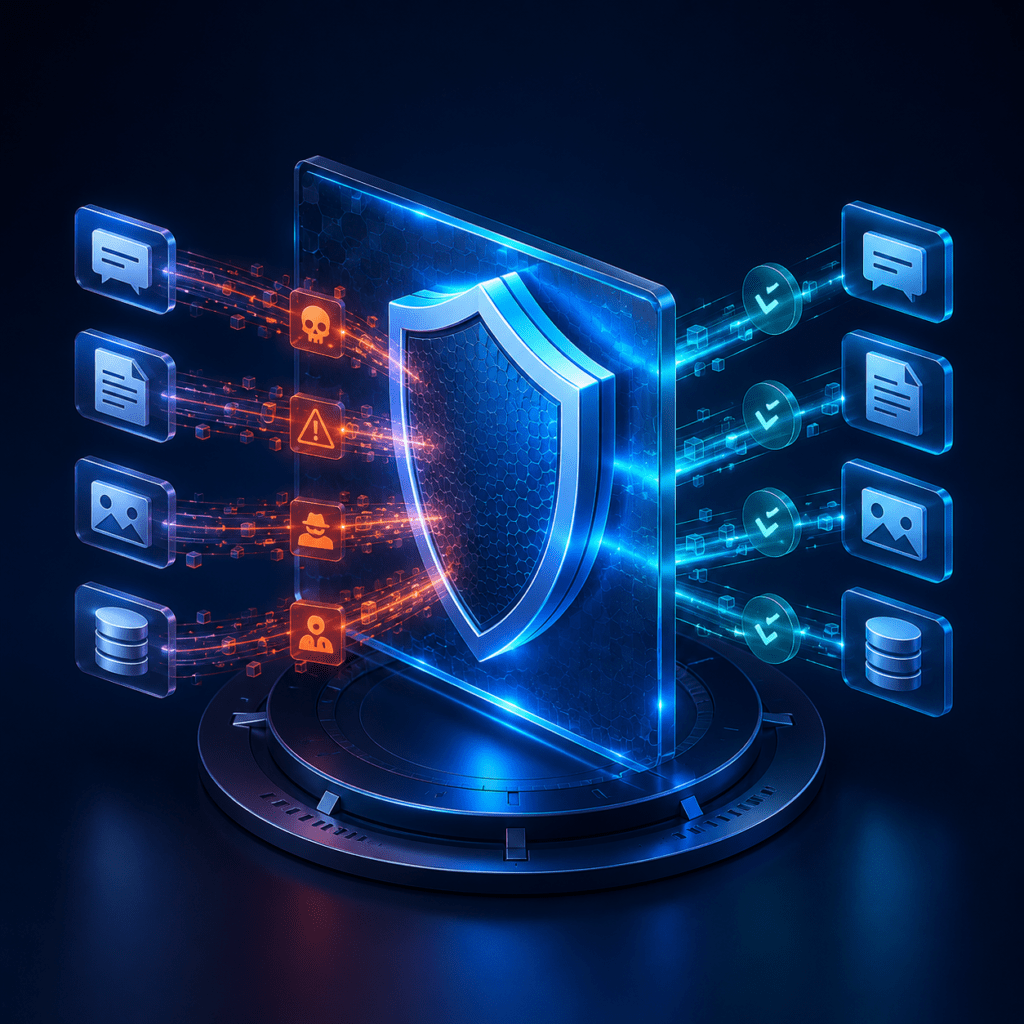
Here is how to secure an internal AI copilot: route every request through one control point. DeepintShield gives the copilot its own Virtual Key, checks prompts and answers with runtime guardrails, limits which models it can use and what it can spend, and records each request, so staff keep a useful assistant without exposing data.
The challenge
Internal copilots spread quickly because they are useful. Staff paste in customer records, contracts, source code and sometimes credentials. The same features that make a copilot helpful also create risk:
- Sensitive data leaves in prompts. Personal data and secrets reach an external model provider, and may be echoed back in answers.
- Provider keys sit in application code. Anyone with the repository can call the model directly, outside any policy.
- Nobody can say who asked what. Without central logs there is no record of usage, cost or blocked content.
- Costs grow unnoticed. A popular copilot or a looping integration can run up a large bill before anyone looks.
The approach
Treat the copilot like any other production application. Give it a single, governed route to models instead of raw provider keys. Check content where it enters and leaves the model. Grant only the models, tools and budget it needs. Keep a record that security and finance can both read. Roll new policies out in shadow mode first, review the findings, then enforce them. This keeps the copilot useful while the controls are tuned on real traffic rather than guesses.
How to secure an internal AI copilot with DeepintShield
- Route the copilot through a Virtual Key. Add your provider keys to the gateway, create a Virtual Key (
sk-ds-...) for the copilot, and point its OpenAI-compatible client athttps://app.deepintshield.com/v1. Restrict the key to approved providers and models, and set a budget and rate limit. Turn on “Enforce Virtual Keys on Inference” so no request goes through without a key. Provider credentials stay on the gateway. See the Virtual Keys docs. - Bind guardrail policies to the key. Start from the OWASP LLM Top-10 guardrail cards, available on every plan. Check prompts at the Input stage for injection, jailbreak attempts, personal data and secrets, and check answers at the Output stage, including streaming output. Run each policy in shadow mode, review what it finds, then switch to sync enforcement. On Team and above you can add the ML detector sidecar. See the guardrails docs.
- Control access and keep the record. Console users sign in with SSO over OIDC (Microsoft Entra ID, Okta, Google Workspace, Auth0 or any OIDC provider), with MFA and role-based access. If the copilot uses MCP tools, its Virtual Key sees only the tools you allow. Built-in logs record tokens, cost, latency and guardrail outcomes; use “Disable Content Logging” if prompts must not be stored.
What you can show afterwards
Once the copilot runs through the gateway, you can answer the questions a security review or budget owner will ask, using records rather than assurances:
- Every copilot request tied to its Virtual Key, with tokens, cost and latency.
- Guardrail findings by stage and status: passed, redacted, blocked or flagged. Blocked requests return HTTP 403
guardrail_blocked. - The list of models the copilot may call, its budget, and the requests refused when a limit was reached.
- Configuration changes in the audit log, which uses a SHA-256 hash chain you can check with “Verify chain”.
Results depend on your traffic and policies, so measure your own baseline in shadow mode before you enforce. The guide to the five stages of LLM guardrails explains which check belongs where.
Related
- Runtime Guardrails & PII: the checks on prompts and answers
- Governance: Virtual Keys, budgets and access rules
- AI governance for global capability centres: copilots shared across many teams
- Stop personal data leaking to LLMs: redact personal data before it leaves
- Give every team safe LLM access: one gateway for every team and app