

AI Logs
Self-Hosted vs SaaS AI Security: Compare Data Flows
Self-Hosted vs SaaS AI Security: Compare Data Flows Choosing where to run an AI security gateway is also a choice about who…
Meet DeepintShield at Bengaluru Tech Summit 2026, 17 to 19 November, BIEC Hall 1, booth H1A106. Book 20 minutes
Government & public sector · Air-gapped option
Sovereign AI security means public bodies can use AI while data, keys and audit records stay in country and under their control. DeepintShield can run fully self-hosted in your cloud or data centre, with an air-gapped option, redacts personal data before it reaches a model and records AI decisions in a tamper-evident log.
Prompts that contain citizen records go to a model hosted abroad, outside national data-residency rules.
A security product that reports back to its vendor is hard to approve for sensitive public-sector work.
When AI drafts a decision or acts on a case, you need a record of what it saw and who approved it.
Switch on presets that already exist in the product, then tune them to your own data.
Guardrails for prompt injection, jailbreaks and sensitive information disclosure, ready to switch on.
Presets for goal hijacking, tool misuse, identity abuse and rogue agent behaviour.
Finds identifiers such as Aadhaar, PAN, SSN and passport numbers, and redacts them before the model.
Finds API keys, private keys, tokens and auth headers, and blocks or redacts them before a model sees them.
Bring a real public-sector workflow. We can show it in the deployment mode you plan, including self-hosted.
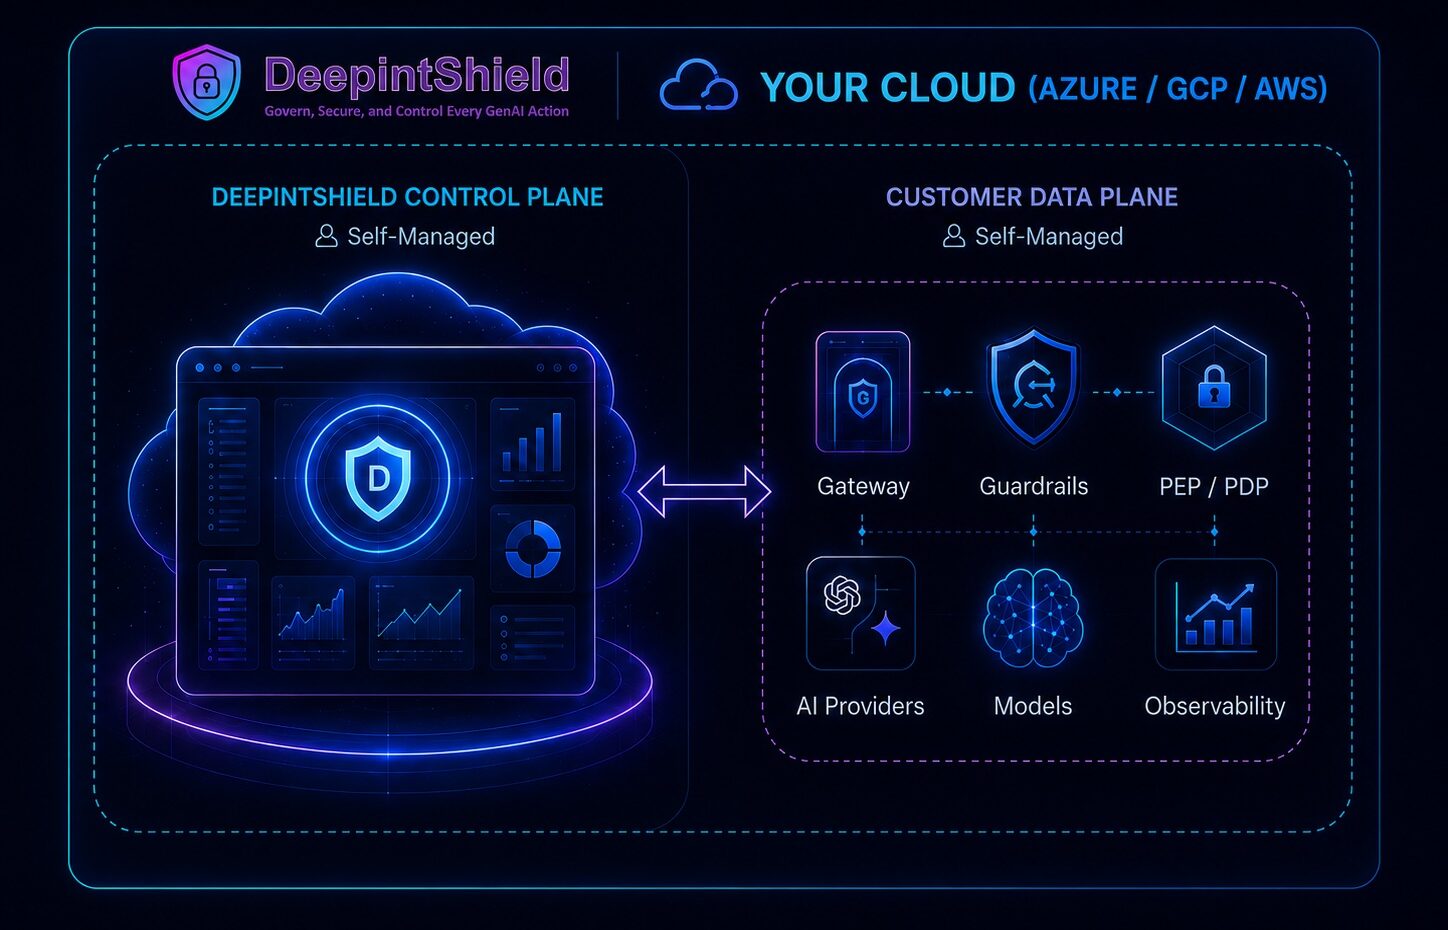
Self-host the full platform in your own cloud or data centre. In self-hosted and hybrid modes, no data leaves your environment, and a self-hosted install does not call home. See self-hosted deployment.
Enterprise Self-Hosted has an air-gapped delivery option. Pair it with models you host through Ollama, vLLM or SGLang so requests stay inside your network.
Bring keys from your own KMS, keep model provider keys on your own accounts and set the HMAC key that seals the audit chain. Production refuses to start without it.
Redaction runs on prompts, responses, RAG chunks and tool calls, inside your deployment, before data reaches a model.
Each governed tool call gets Allow, Deny or Require approval, and approvers cannot be the requester. Agentic Security is on Business and above.
A hash-chained ledger, Verify chain and JSON or CSV exports give auditors records they can check for themselves.
3
deployment options
Cloud, Enterprise VPC and Self-Hosted
460+
detection patterns
462 entries in 102 preset families
5
enforcement stages
Input, RAG, Action, MCP and Output
730 days
default evidence retention
for the agent decision ledger
Product facts from the DeepintShield docs, not customer results. Pattern counts are configuration entries, not a measure of accuracy.
Give staff an AI assistant with redaction, access control and a full audit record.
Read the use case
Redact citizen identifiers such as Aadhaar and passport numbers before any prompt reaches a model.
Read the use case
Show oversight bodies a verifiable record of what AI systems and agents did.
Read the use case
Mapped to
Product facts
Mappings support your own assessment; they do not replace it. The open-source core is published under the Apache License 2.0. Compare other regulated industries.
Yes, on Enterprise Self-Hosted. Air-gapped delivery is an option on that plan, and with self-hosted models served through Ollama, vLLM or SGLang, requests need not leave your network. Read the deployment overview.
Not when you self-host: a self-hosted install does not call home. In hybrid (Enterprise VPC), no prompt, response, key or audit data leaves your VPC; only signed configuration comes down and aggregate counts go up, over one outbound-only mutual-TLS connection.
You do. Enterprise VPC uses keys from your own KMS, model provider keys stay on your accounts, and you set the HMAC key that seals the audit chain.
By keeping data where you run it. Self-hosted and VPC deployments keep prompts, responses, keys and audit records in the location you choose. Your legal team decides which deployment meets which rule.
It helps; it does not make you compliant. Capabilities are mapped to the EU AI Act, NIST AI RMF and ISO/IEC 42001, and the audit log supports evidence for oversight. See how the mapping works.
Self-Hosted vs SaaS AI Security: Compare Data Flows Choosing where to run an AI security gateway is also a choice about who…
DeepintShield team · · 5 min read
A hash-chained audit log records every decision in a way that makes tampering detectable: each entry includes a cryptographic hash of the…
DeepintShield team · · 4 min read
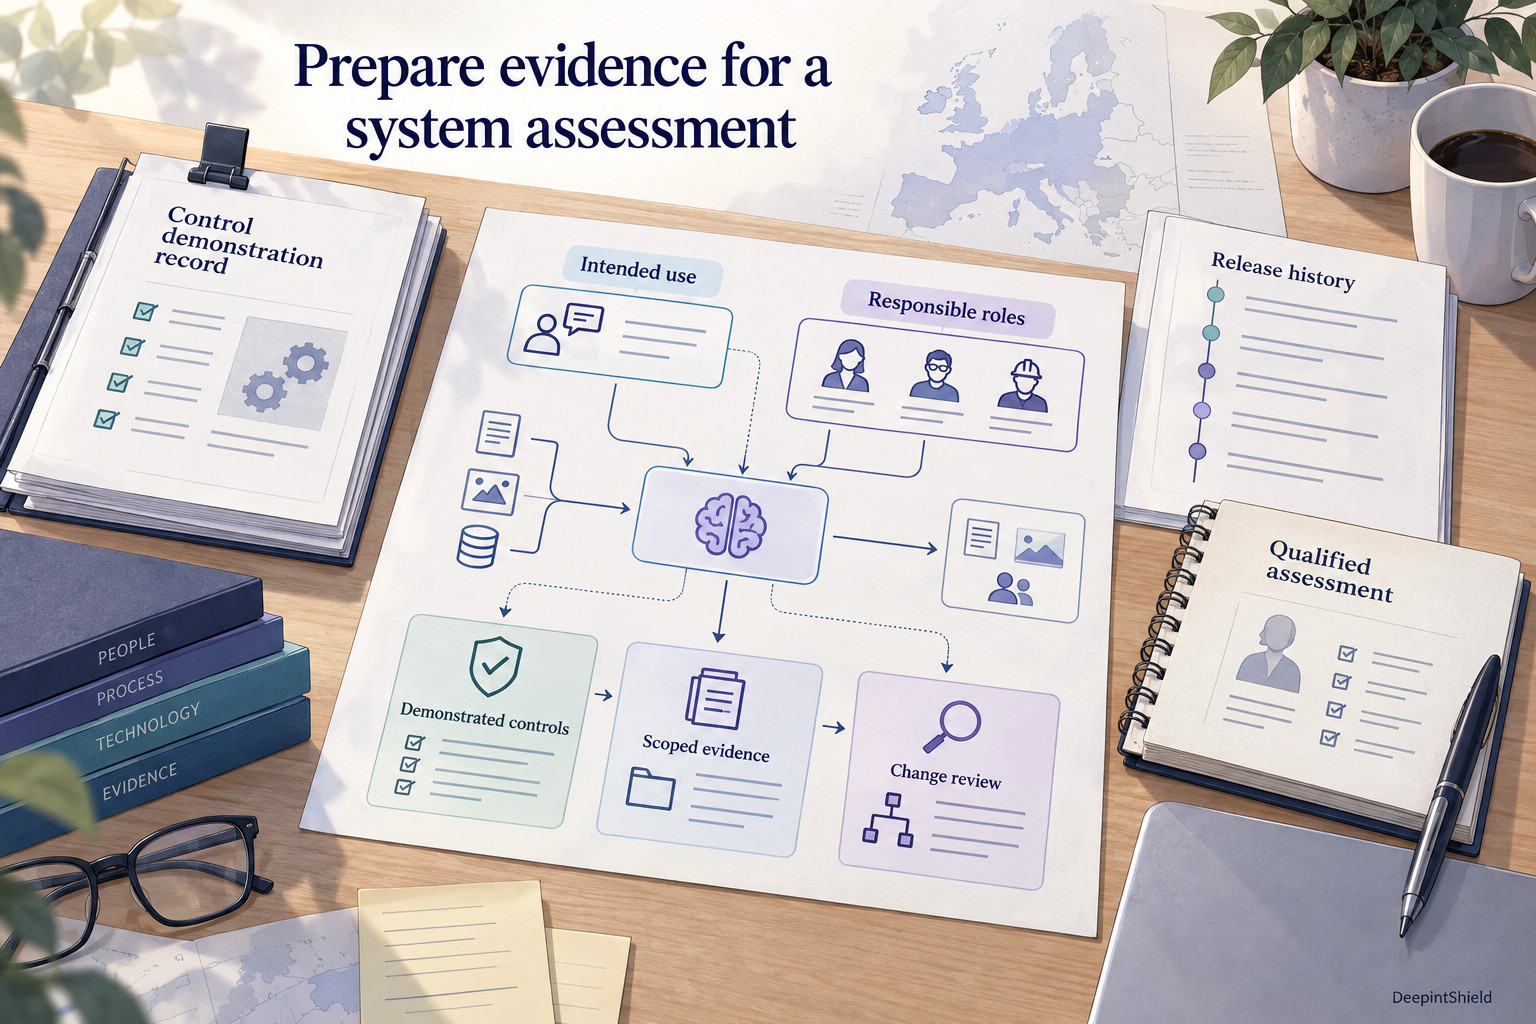
EU AI Act Readiness: Practical Controls for GenAI EU AI Act readiness begins with a clear account of what a system does…
DeepintShield team · · 5 min read
Tell us where the platform must run and which rules apply. We will walk you through a sovereign deployment.